From 112 Critical Vulnerabilities to Zero:
Building a Layered Security Posture for a Healthcare SaaS Platform
Snyk and SonarQube in every pull request, Datadog and Invicti watching running code, Nessus inside the network, Security Onion in front of it and Resecurity watching the dark web — six layers, one view, no new headcount.
 🔍 Expand Snyk Baseline View
⚠️ The Challenge
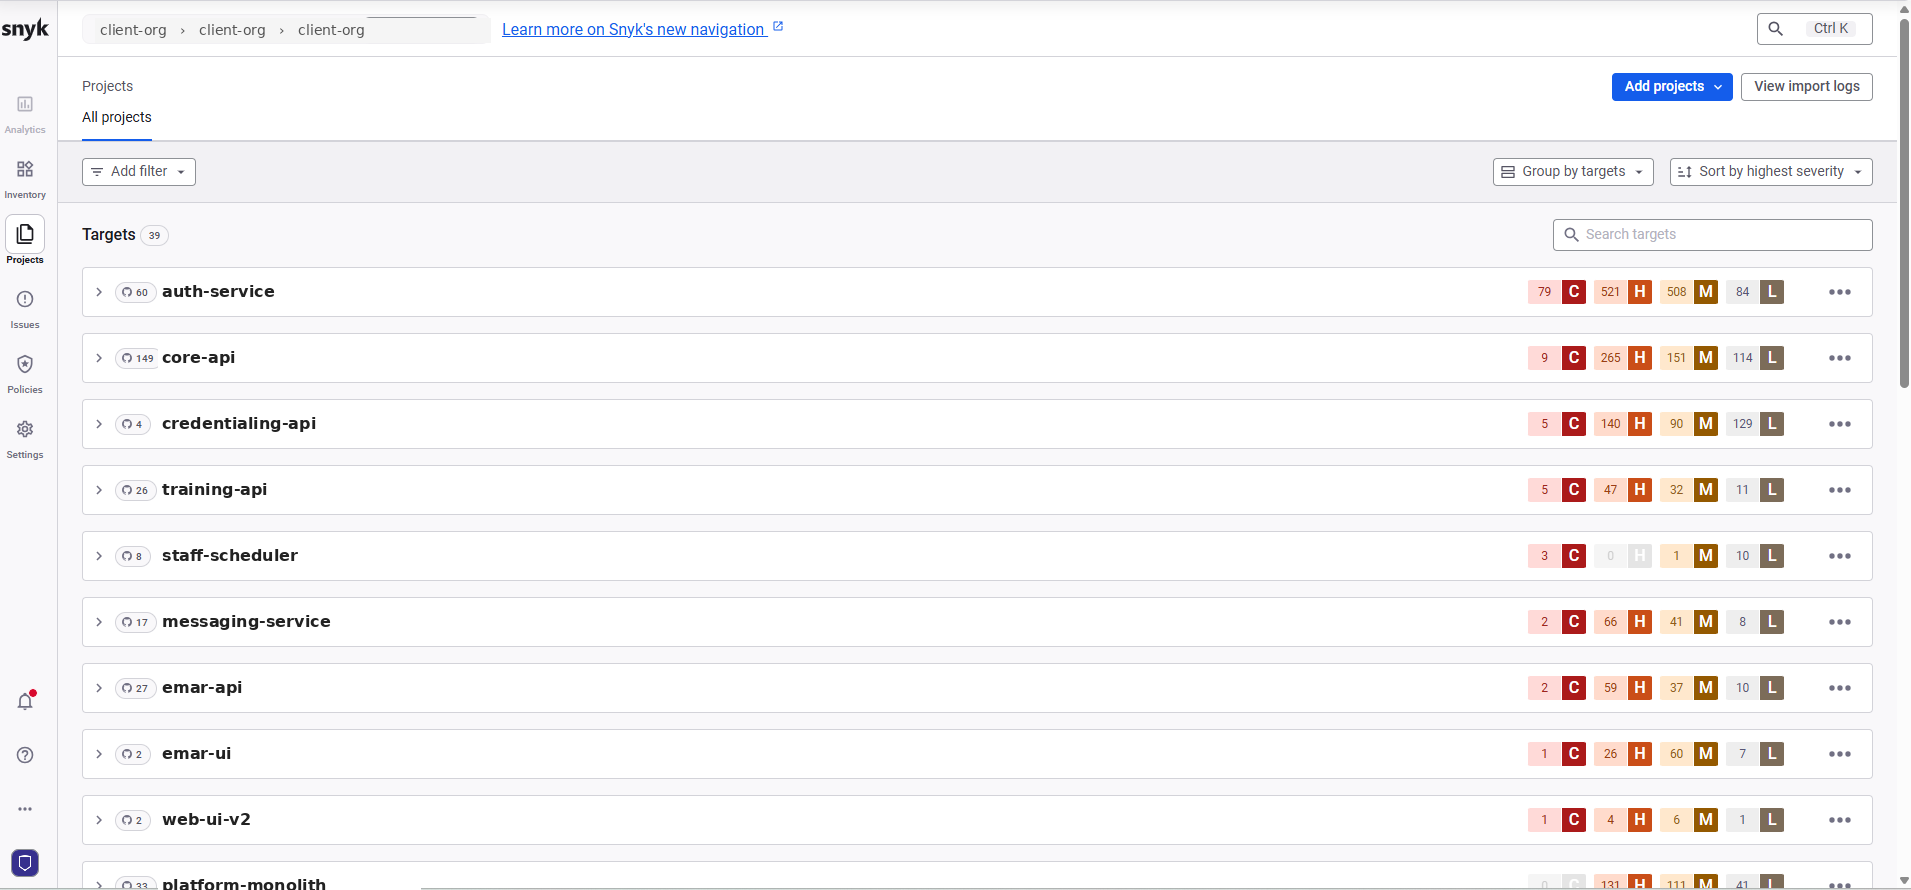
After migrating to containers, the platform deployed dozens of times a week, but security had not kept pace. There was no pipeline scanning—the first Snyk baseline revealed 112 critical and ~1,200 high-severity findings across 39 repositories.
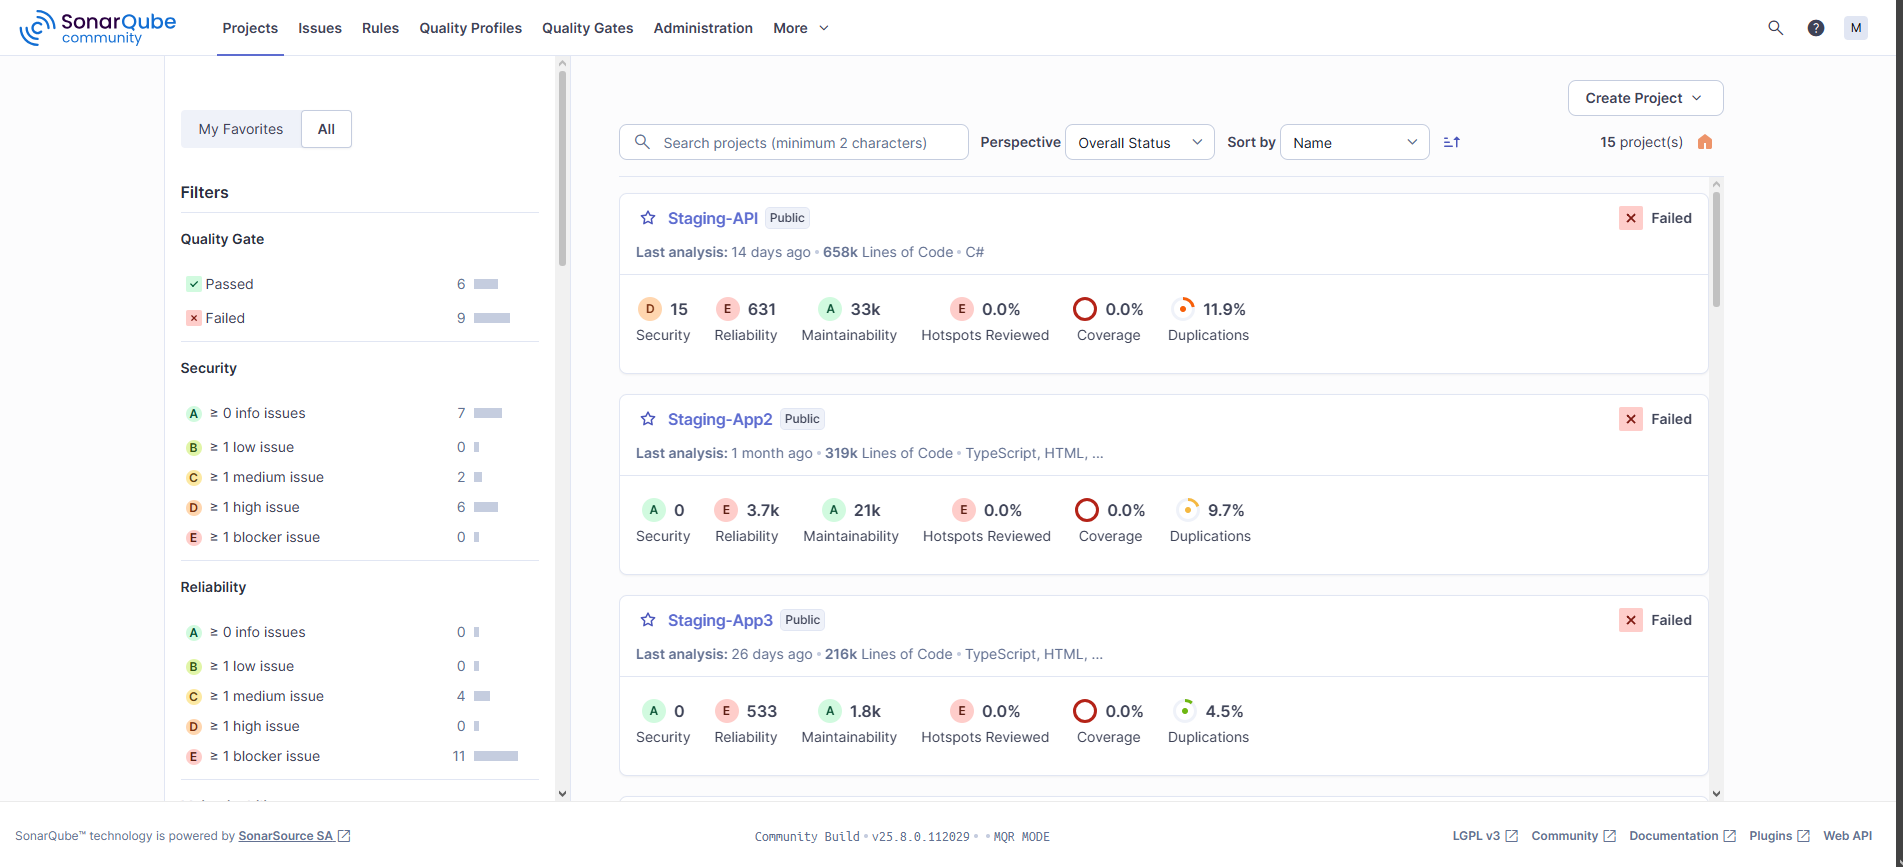
9 of 15 SonarQube projects failed quality gates, 149 open web vulnerabilities existed (including CORS misconfigurations across 256 endpoints), and mean time to remediate (MTTR) sat at 4.8 months. No internal host scanning, intrusion detection, or dark-web monitoring was present, threatening annual SOC 2 and HIPAA compliance audits.
⚡ The Cyber Oxygen Approach
We engineered a comprehensive, 16-week 6-layer DevSecOps and cloud security posture:
- Exploitability Triaging & SLAs (Weeks 1–3): Prioritized findings reachable in production. Set strict SLAs: Critical 72h, High 14 days.
- Shift-Left PR Scanning (Weeks 3–6): Embedded Snyk & SonarQube into GitHub Actions with fail-on-critical gates. Auto-fixed 82 unassigned criticals in month 1.
- Runtime Code & DAST Testing (Weeks 5–9): Instrumented Datadog IAST to pinpoint 80 vulnerabilities actually loaded in production. Configured Invicti DAST for automated release scans.
- Internal Vulnerability & NDR (Weeks 8–13): Deployed monthly Tenable Nessus scans and Security Onion (Suricata inline IPS + Zeek metadata) on cloud VNets.
- Dark Web Threat Intel (Weeks 12–16): Integrated Resecurity for continuous dark-web monitoring across 15 domains, catching and resetting leaked staff credentials within 4 hours.
Quantified Security Impact (12-Month Comparison)
| Measure | Before Cyber Oxygen | After Cyber Oxygen |
|---|---|---|
| Critical vulnerabilities (Snyk) | 112 | 0 |
| High-severity vulnerabilities (Snyk) | ~1,200 | 19 (all with owners, inside SLA) |
| Libraries with critical / high CVEs | 111 (5 end-of-life) | 4 (0 end-of-life) |
| SonarQube projects passing quality gate | 6 of 15 | 15 of 15 |
| Open web-app vulnerabilities (Invicti) | 149 (2 high) | 11 (0 critical, 0 high) |
| Mean time to remediate (High severity) | 4.8 months | 9 days |
| Internal scan critical findings (Nessus) | Never scanned | 0 open > 7 days; 100% SLA |
| Mean time to detect intrusion attempt | No detection | 3.6 min (IPS blocks ~95% inline) |
| Leaked credentials detected / reset | Unknown | 2 exposures caught, reset < 4 h |
| SOC 2 / HIPAA evidence preparation | 2–3 weeks, manual | Under 1 day, tool exports |
Layered Defense & Telemetry Proof Elements
 🔍 Expand SonarQube Report
SonarQube Quality Gate Baseline
Project overview at baseline showing 9 of 15 projects failing quality gates, burdened with unreviewed security hotspots and blocker reliability issues.
 🔍 Expand Datadog IAST
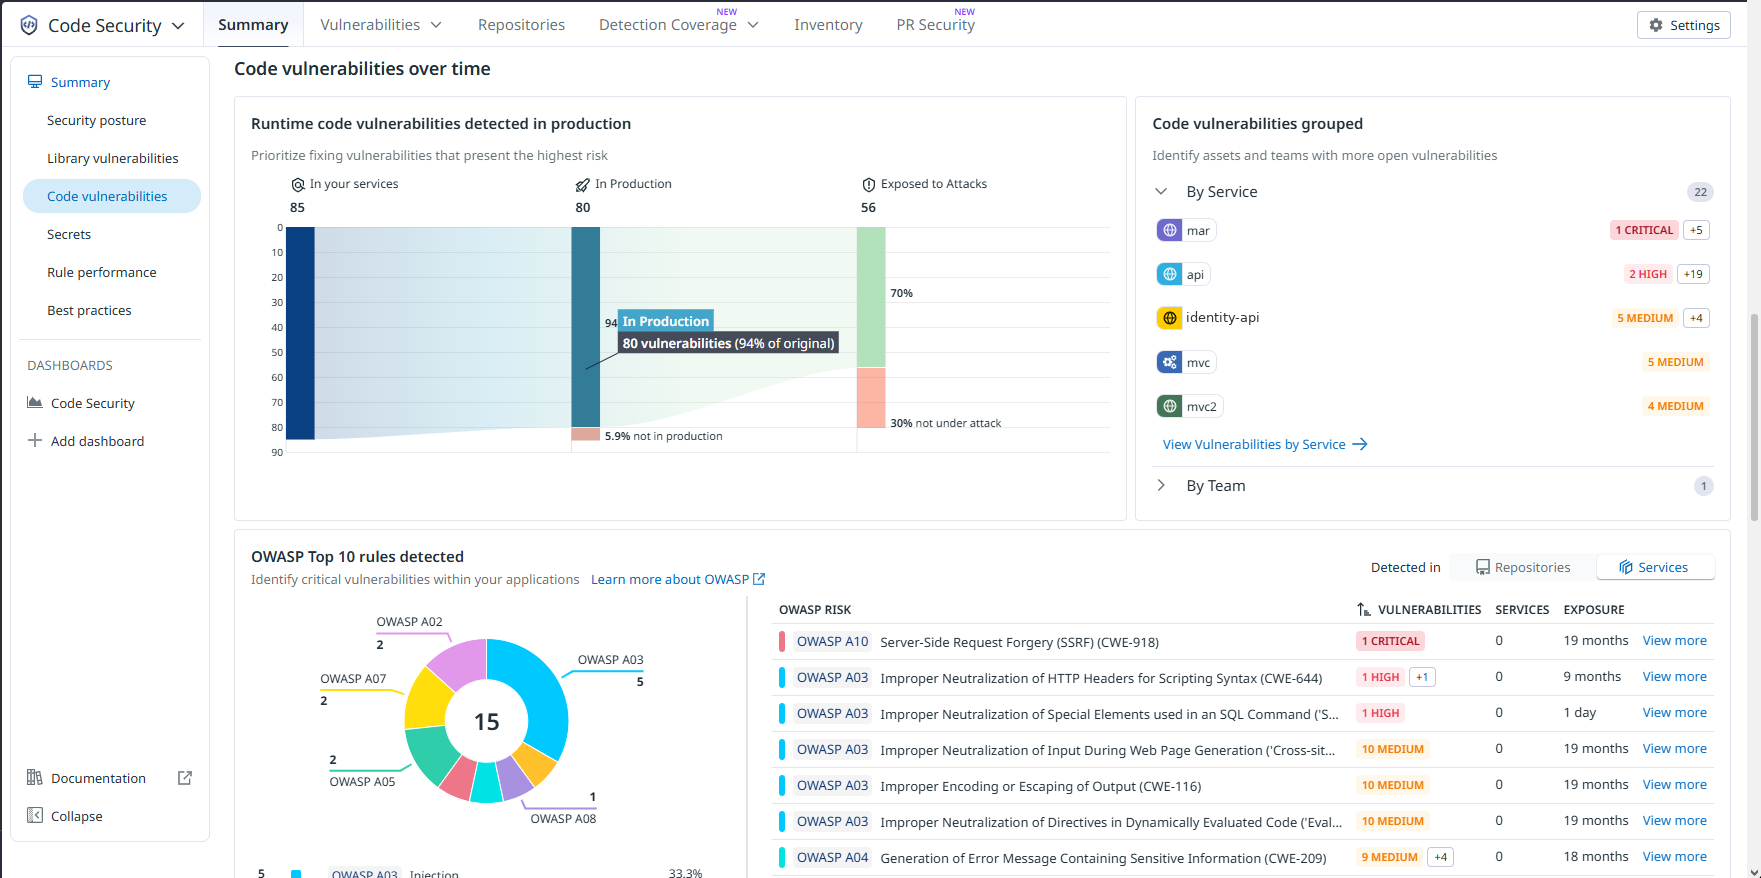
Datadog Runtime IAST Analysis
IAST instrumentation distinguishing the 80 vulnerabilities actually loaded in production from default branches, isolating 56 exposed to active attack traffic for immediate resolution.
 🔍 Expand Library Breakdown
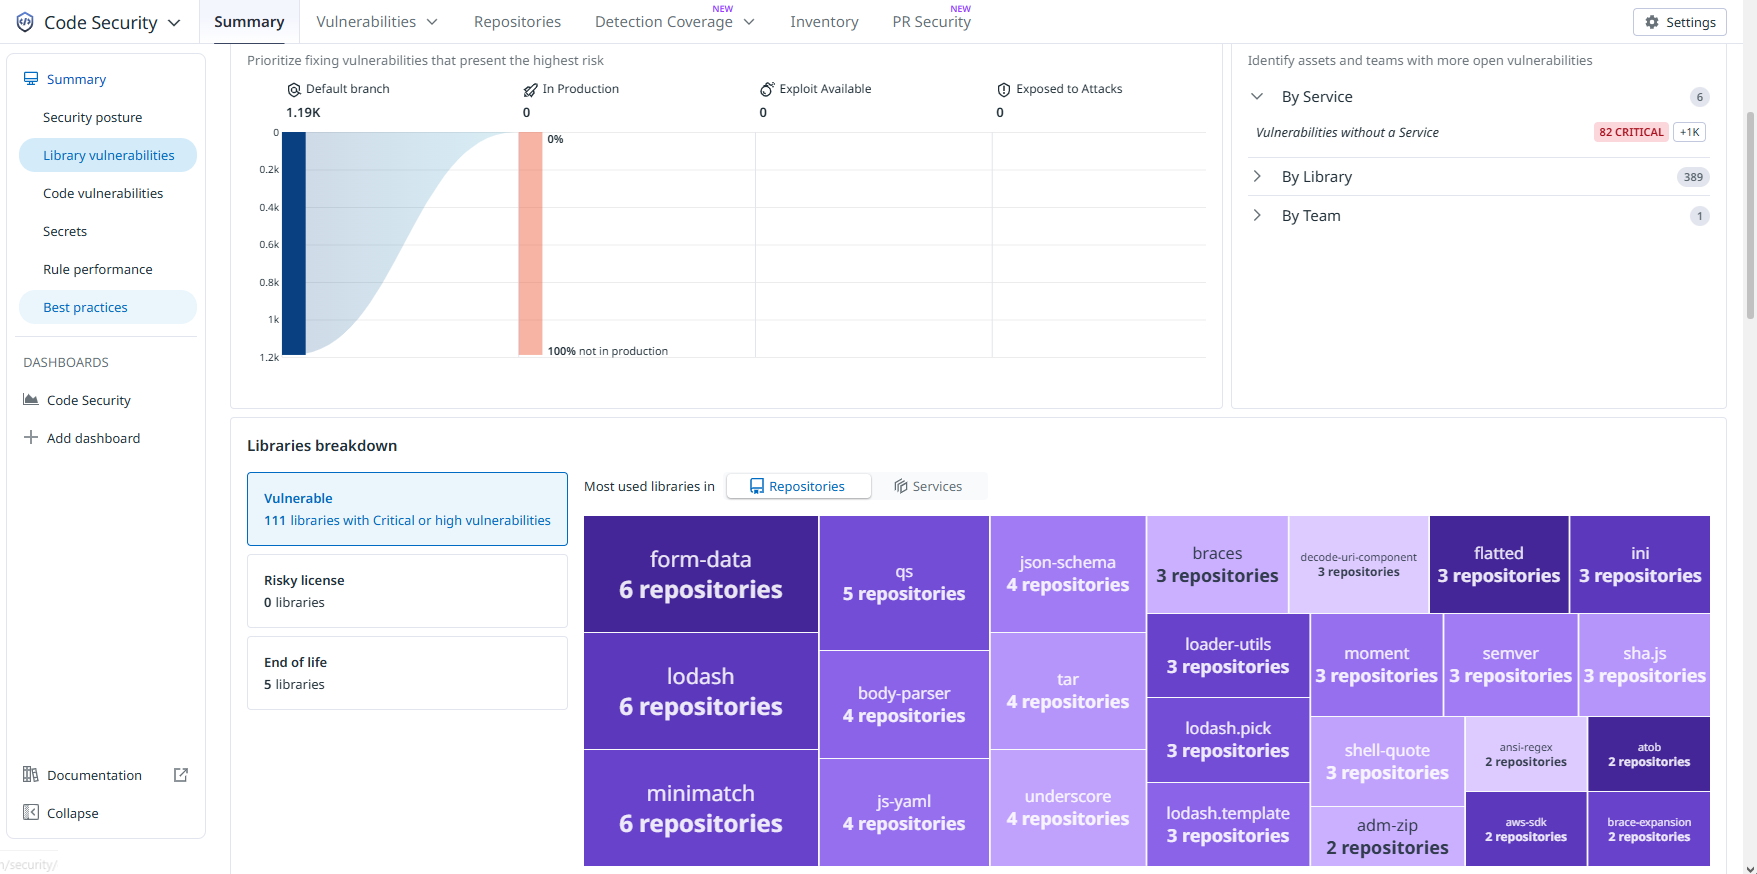
Datadog Library Vulnerability Breakdown
Mapping 1,190 default branch findings down to zero in production, identifying and eliminating widespread vulnerable dependencies like form-data, lodash, and minimatch.
 🔍 Expand Invicti Summary
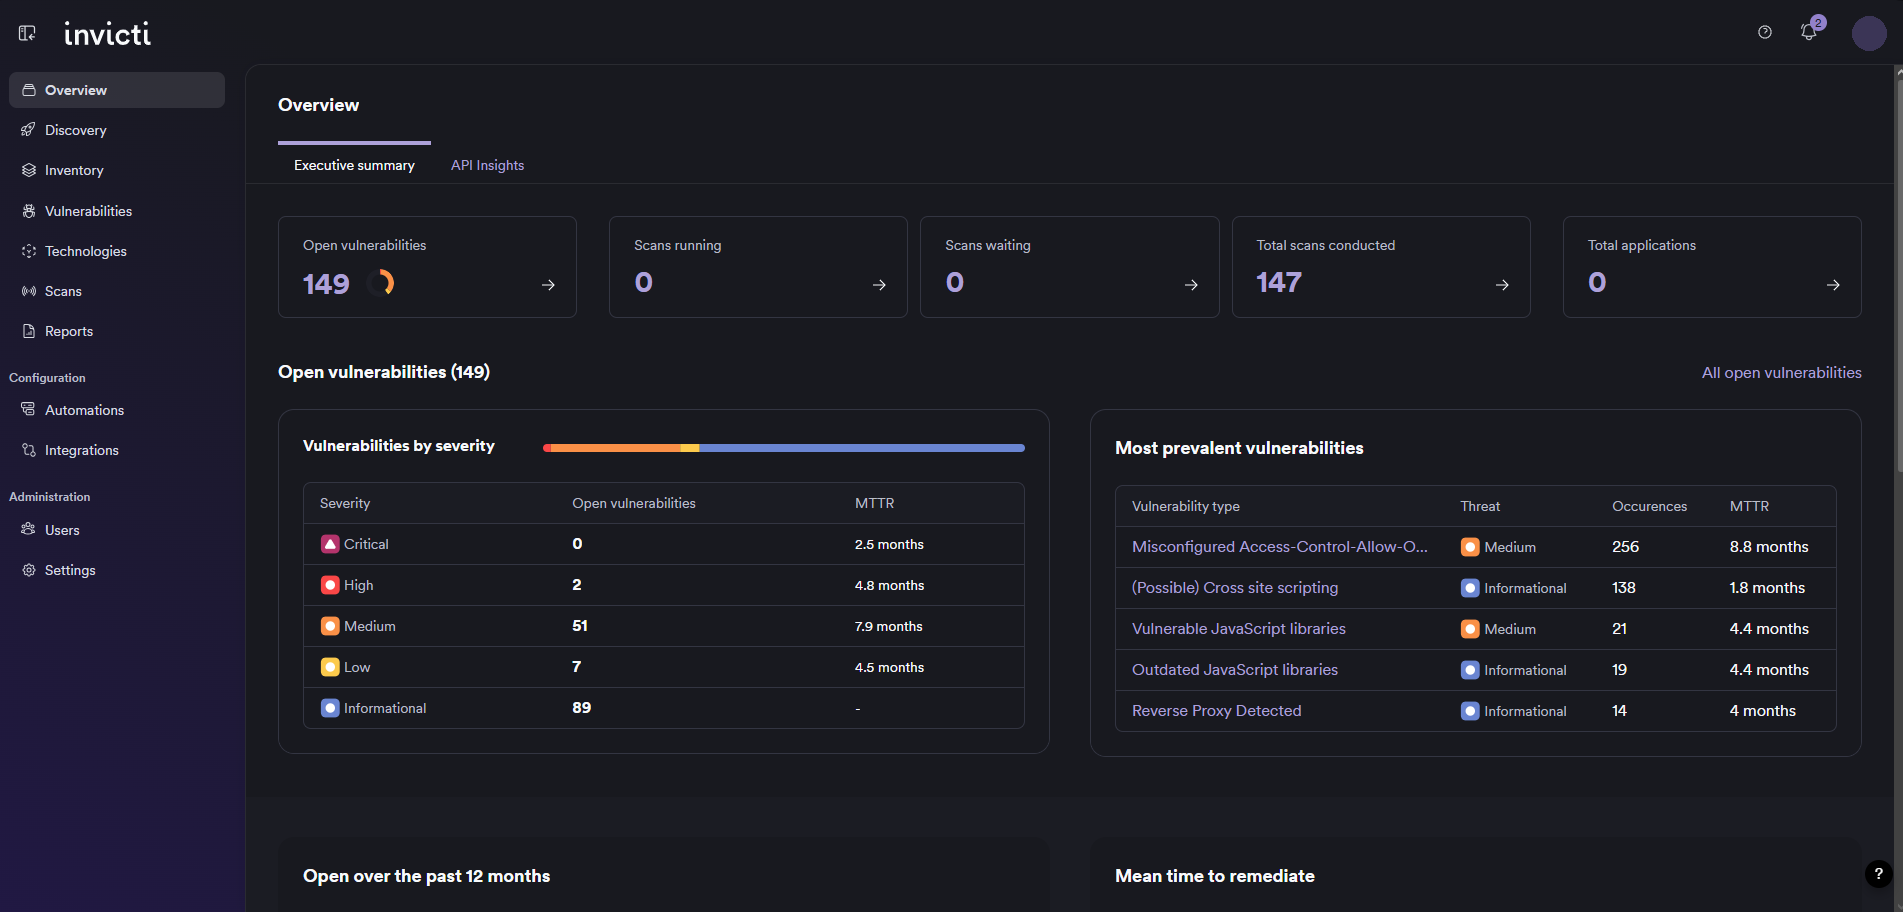
Invicti Automated DAST Scans
Executive summary following remediation across 147 scans, driving open criticals down to zero and mitigating prevalent CORS misconfigurations across API endpoints.
 🔍 Expand Nessus Internal View
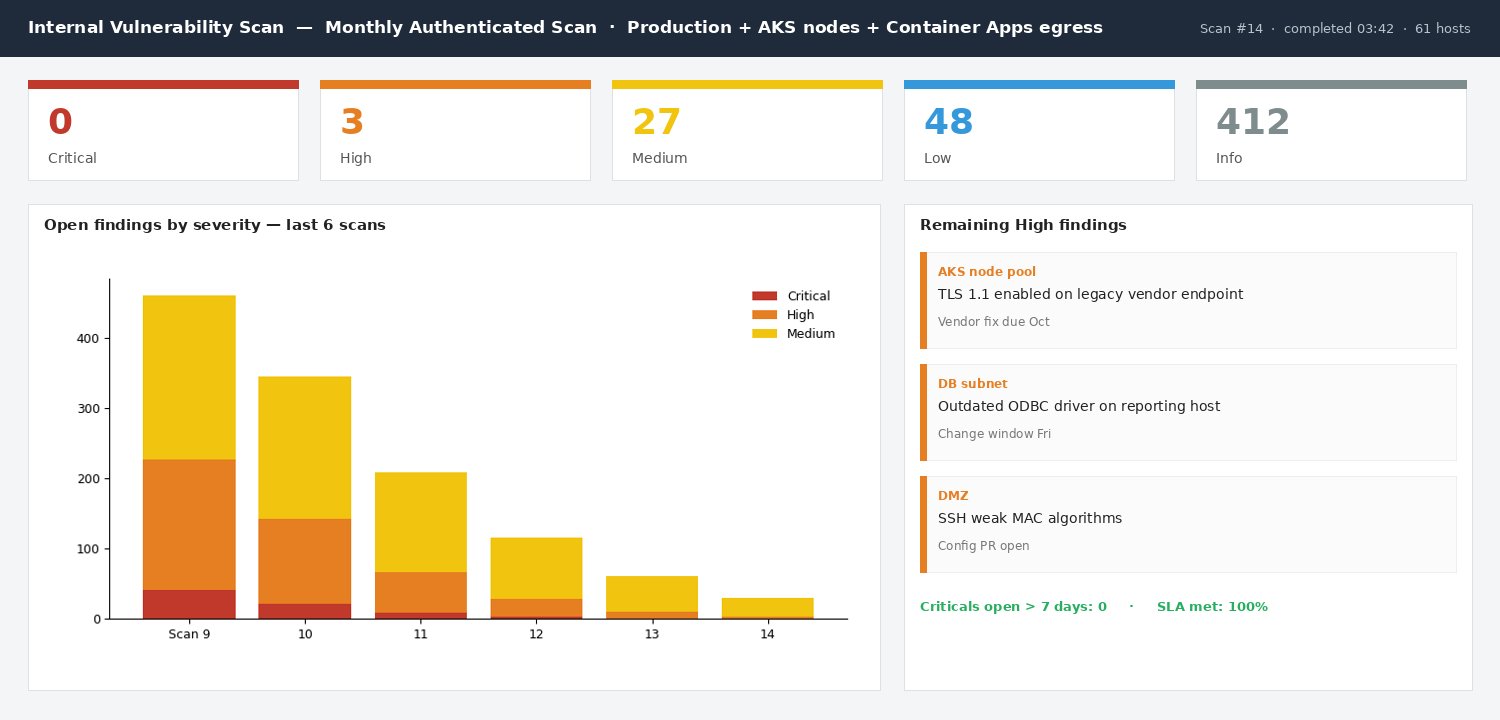
Nessus Monthly Internal Host Scans
Authenticated scans across 61 hosts, AKS node pools, and DB subnets—driving critical vulnerabilities to zero over 6 scan cycles with 100% SLA compliance.
 🔍 Expand Security Onion Dashboard
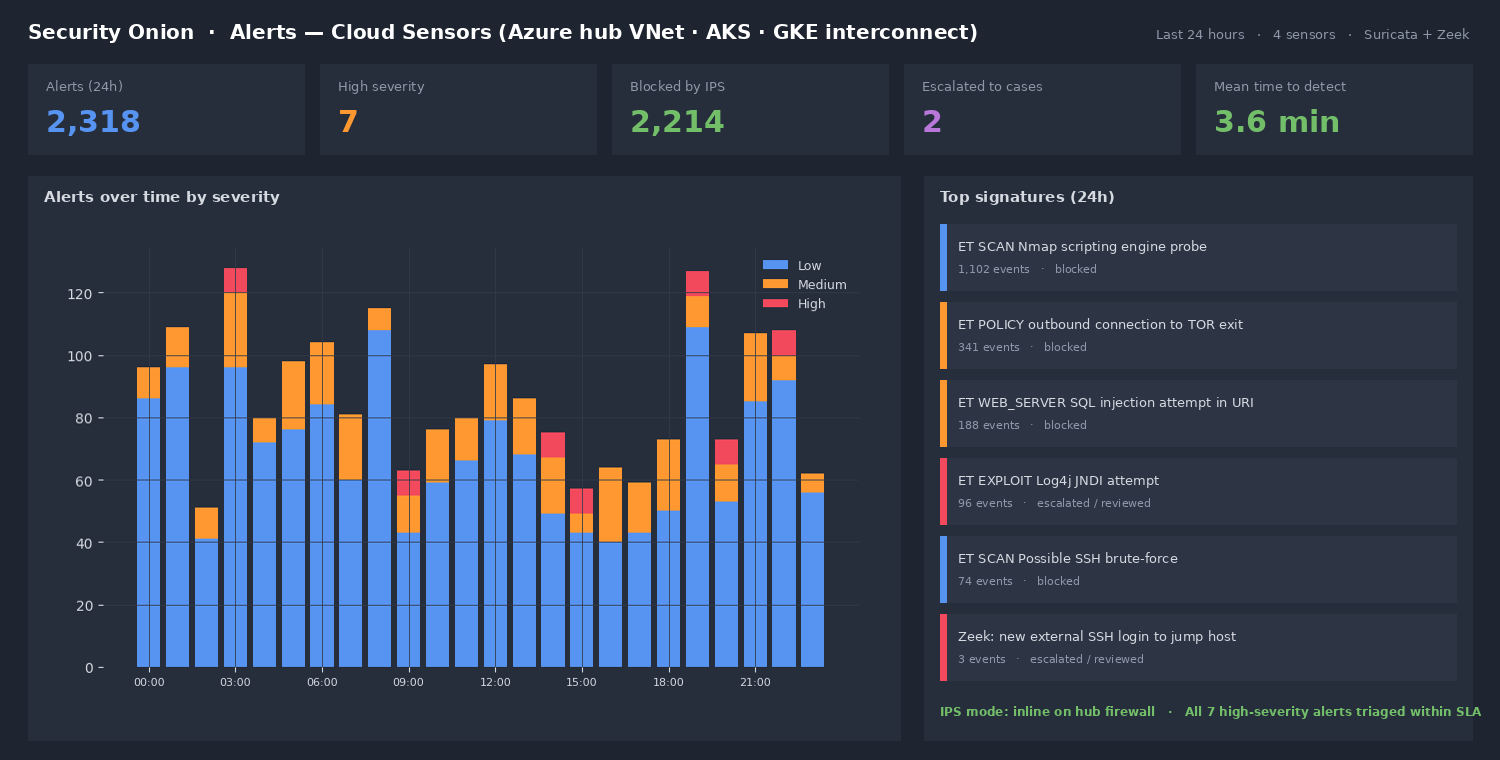
Security Onion NDR & Cloud Telemetry
Cloud sensors capturing 2,318 daily alerts with Suricata blocking 2,214 attacks inline, providing a 3.6-minute mean time to detect intrusion attempts.
 🔍 Expand Resecurity View
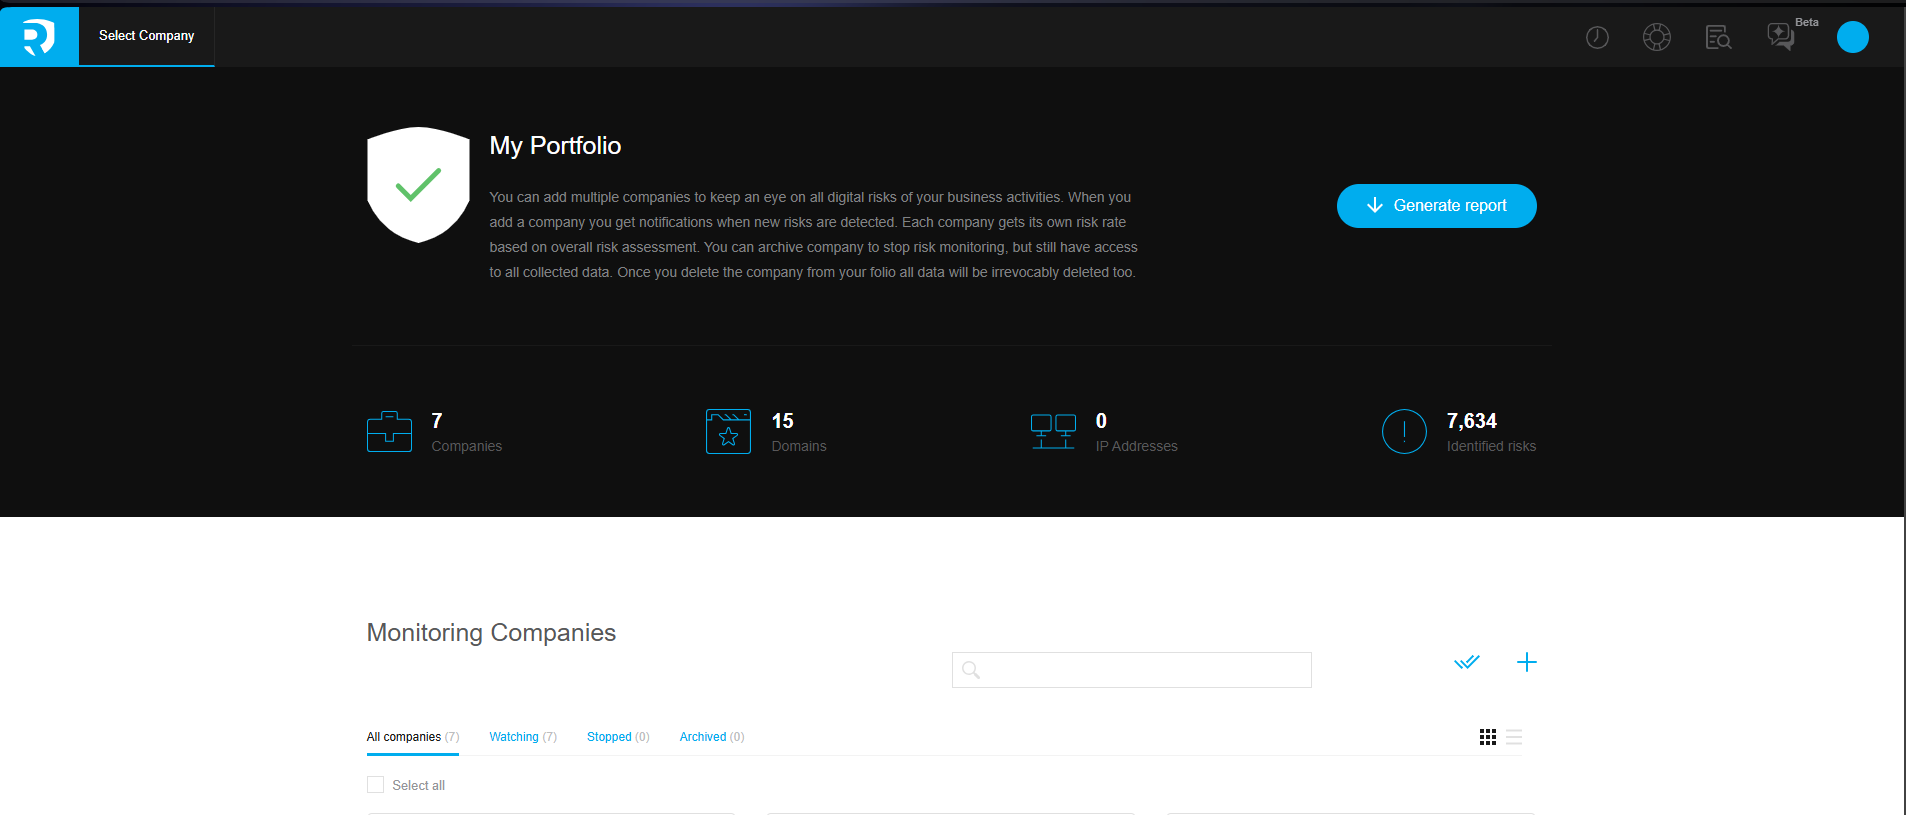
Resecurity Dark Web Risk Intelligence
Continuous external intelligence monitoring 15 domains and staff identities, detecting and neutralizing exposure risks before exploitation.
“Our auditors used to get a folder of screenshots we spent three weeks assembling. This year they got read-only logins and finished in a day. The engineers fix things before I even hear about them.”
Shipping Fast Without Knowing What’s Vulnerable, Exposed, or Leaked?
Partner with Cyber Oxygen to establish multi-layered security gates, automate compliance evidence, and protect your cloud applications.
Book a 30-Minute Security Posture Review